AgentShield
AgentShield checks every action an AI agent wants to take on a machine, before the action runs, and answers allow, audit or block.
- It runs where the agent runs. It runs on a developer laptop, a CI runner or a server. The decision is made on that machine.
- It is deterministic. Rules are YAML, evaluated by a fixed pipeline, so the same command gets the same answer every time. AgentShield never calls a language model to decide.
- It works offline. If you never sign in, AgentShield makes no network calls at all.
- It explains itself. Every decision names the rule that fired and the reason, so a blocked agent, the developer and your security team all see the same "why".
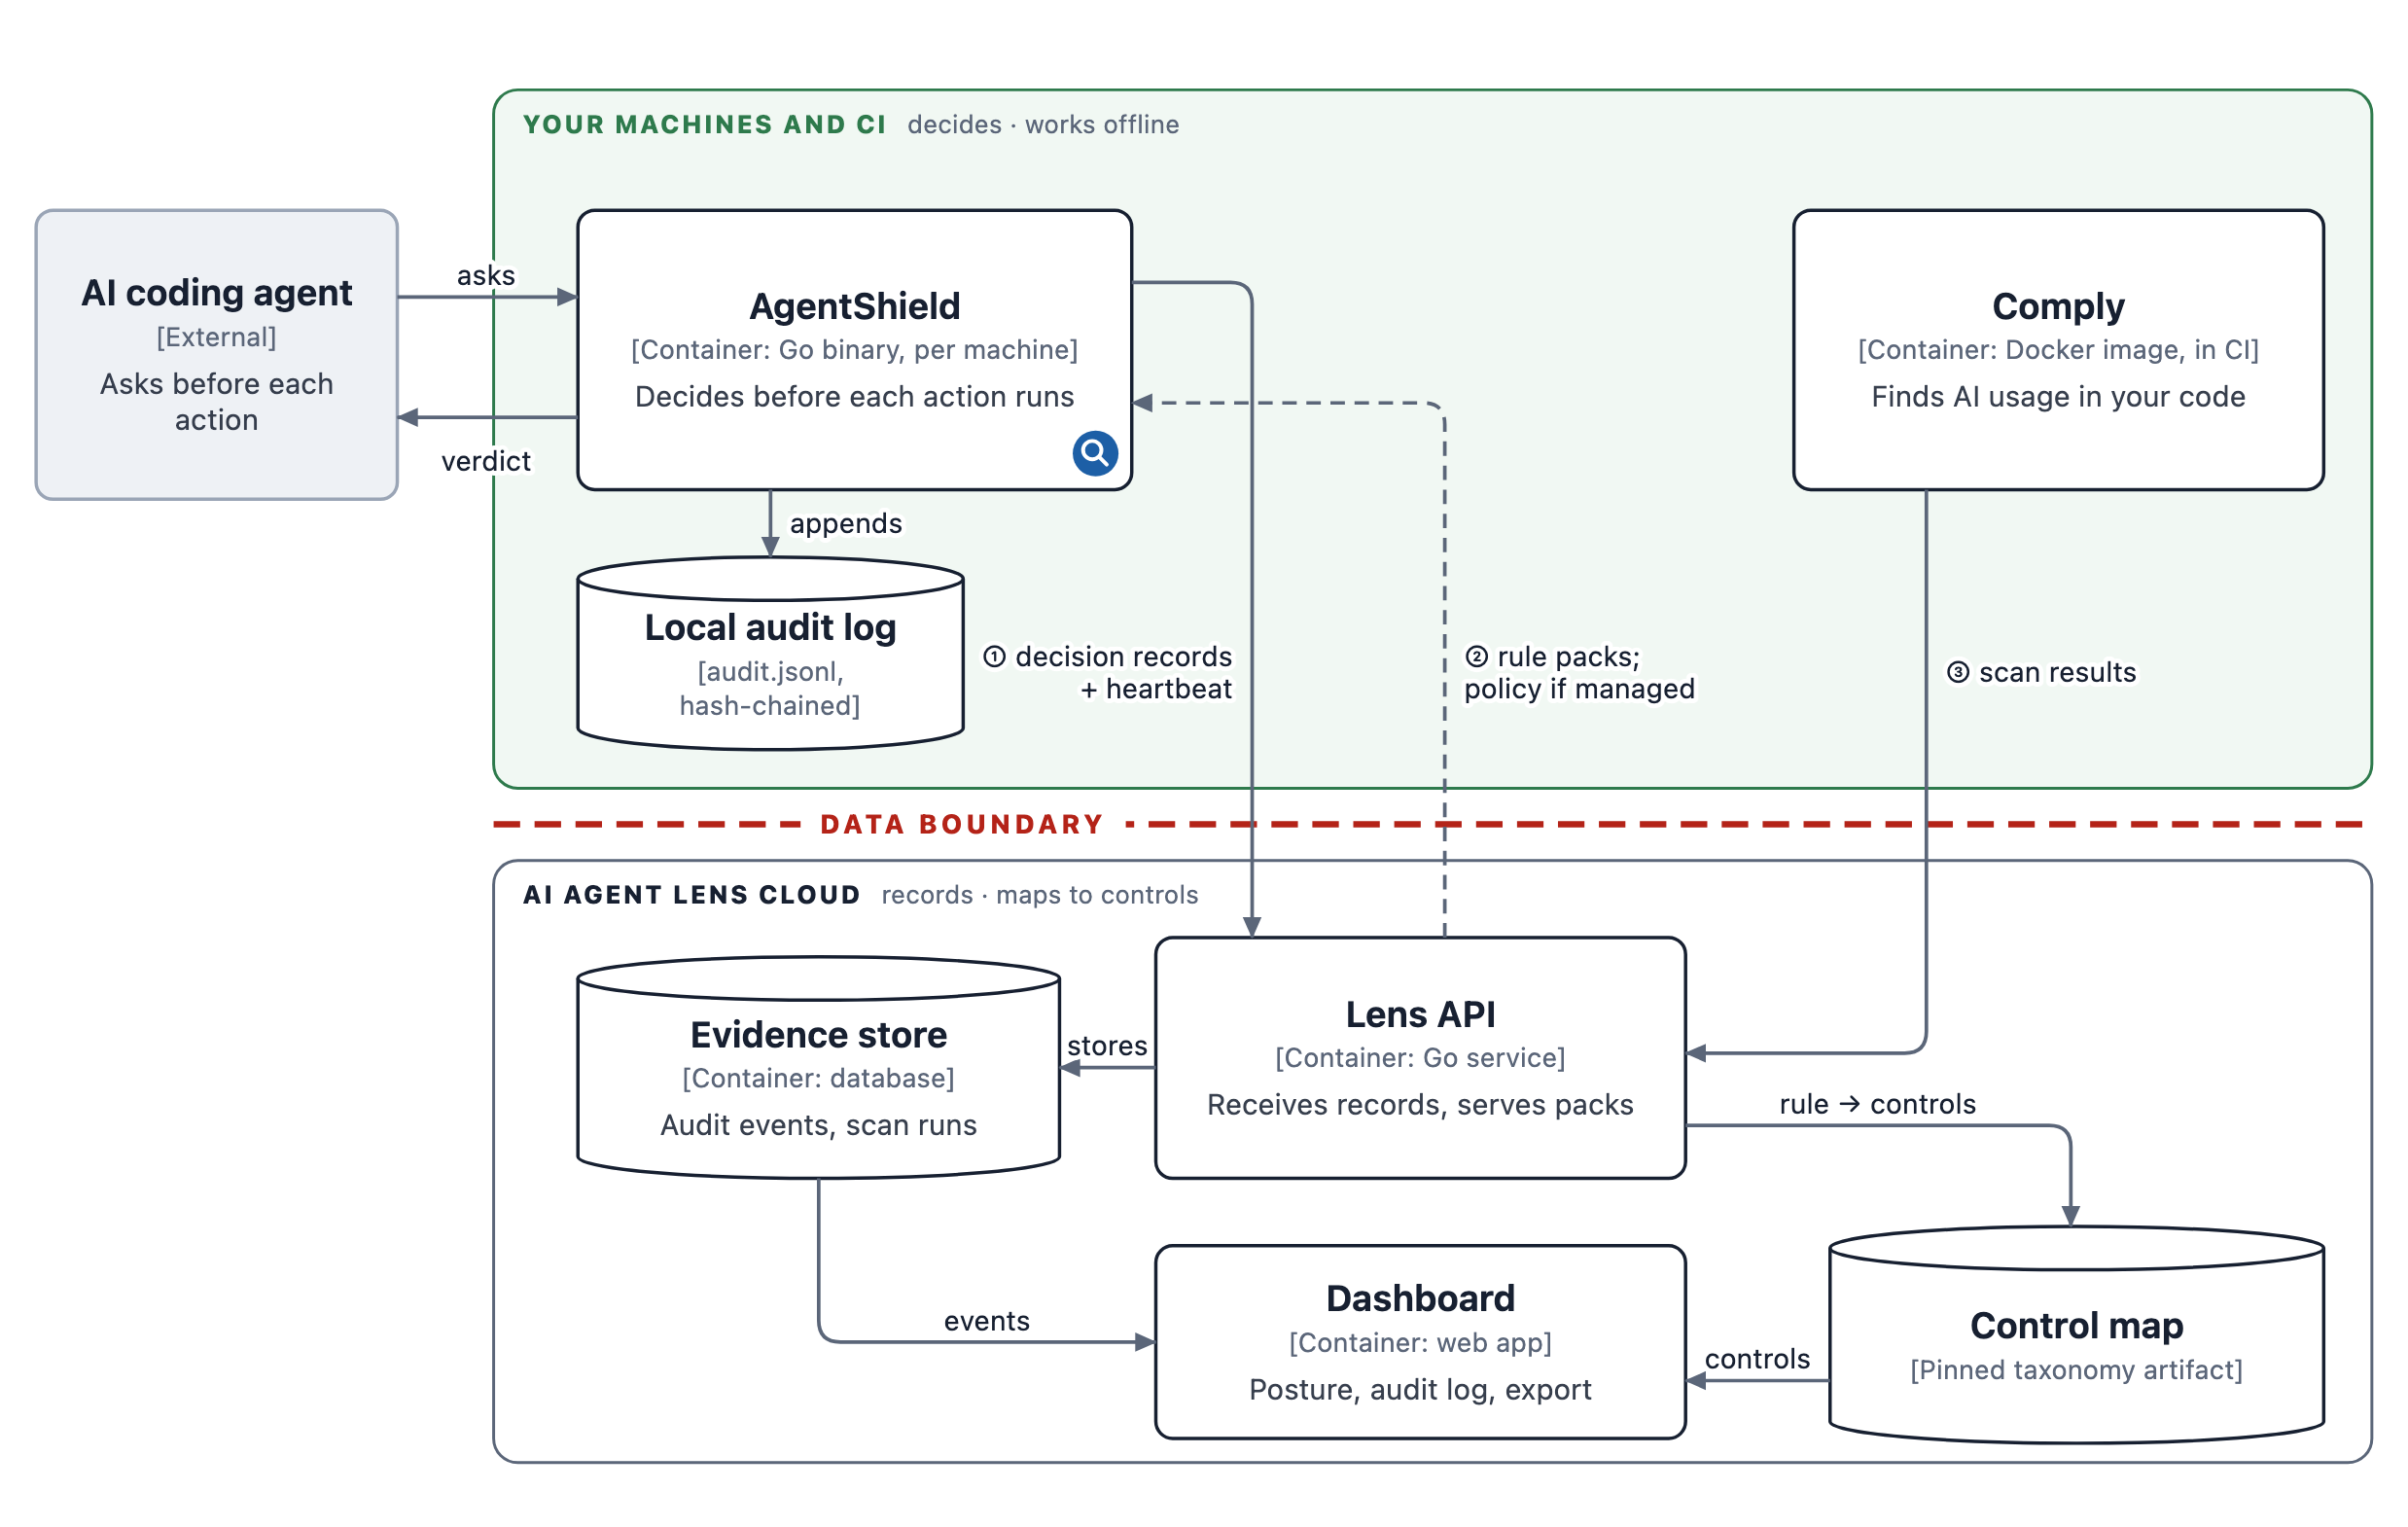
The same picture at every level of detail, zoomable: open the interactive architecture.
What it sees, per agent
Each agent exposes a different hook, so coverage is not identical. This table is what agentshield setup <agent> installs today.
| Agent | Setup command | What AgentShield checks |
|---|---|---|
| Claude Code | agentshield setup claude-code | Every tool call: shell commands, file reads and writes, and MCP tools |
| GitHub Copilot CLI | agentshield setup copilot-cli | Every tool call: shell commands, file edits, and MCP tools |
| OpenAI Codex CLI | agentshield setup codex | Shell commands |
| Gemini CLI | agentshield setup gemini-cli | Shell commands |
| Cursor | agentshield setup cursor | Shell commands. Add agentshield setup mcp for its MCP servers. |
| Windsurf | agentshield setup windsurf | Shell commands |
| Claude Desktop | agentshield setup mcp | MCP tool calls, through a local proxy |
OpenClaw is also supported. Its hook needs files from the source repository, so see Agent and IDE integration.
For an agent whose hook covers only shell commands, its file and MCP tools are not checked unless those MCP servers are wrapped with agentshield setup mcp. If an agent you rely on is in that position, put its MCP servers behind the proxy, or run it behind a Shield server.
Two ways in
| Agent hook | MCP proxy | |
|---|---|---|
| How | The agent asks AgentShield before each tool call (PreToolUse and equivalents). | AgentShield sits between the agent and an MCP server, and checks each call and each tool description. |
| Rules | Shell rules for commands; MCP rules for tool calls the hook forwards. | MCP rules, plus scanners for poisoned tool descriptions and sensitive arguments. |
| Audit-only mode | Honoured, except for part of self-protection, such as deleting AgentShield's audit log, which still blocks; see what still blocks in audit-only. | Honoured for tool calls, except for self-protection: changes to AgentShield's and the agents' configuration still block. Other MCP requests behave as in enforce mode. |
| A suspicious tool description | Not applicable | The tool is removed from the list the agent sees, and recorded as BLOCK, in either mode |
New installs start in audit-only; see what still blocks in audit-only.
A third way, for enterprises (pilot): run Shield at a gateway your company owns, between agents and the model provider. Every tool call a model proposes is checked before the agent receives it, whatever is installed on the laptop. It runs either as a guardrail in an LLM gateway or as network inspection behind a VPN. Each has a tested reference deployment; other components that meet the published requirements fit the same design but are not yet tested. See Enterprise gateway.
Open source and paid plans
The engine is the same in both: the open-source build and the build paying customers install run the same analyzer pipeline. What differs is the rules and what happens to the record.
| Open source | AI Agent Lens plans | |
|---|---|---|
| Engine: all analyzer stages, MCP proxy, local hash-chained audit log | ✓ | ✓ |
| Community rules (about 1,400: 824 shell, 554 MCP) | ✓ | ✓ |
| Premium rules (about 2,300 more: 751 shell, 1,547 MCP) | ✓ | |
| Decisions from every machine in one organisation audit log | ✓ | |
| Each decision mapped to compliance controls (how) | ✓ | |
| Organisation policy and enforcement mode synced to managed machines | ✓ |
Rule counts were taken from the repository's own counter on 2026-10-13; they grow most weeks.
Next
- Install and see a first block, in a few minutes.
- Architecture, for what runs where, what leaves the machine, and what happens when something fails.
- Enterprise gateway (pilot), to enforce at a gateway your company owns.
- Policy authoring guide, to write your own rules.
- Standards, risks and languages: the compliance standards, threat areas and agents covered.